

A DDoS mitigation service supplier in Europe was focused in an enormous distributed denial-of-service assault that reached 1.5 billion packets per second.
The assault originated from hundreds of IoTs and MikroTik routers, and it was mitigated by FastNetMon, an organization that gives safety in opposition to service disruptions.
“The assault reached 1.5 billion packets per second (1.5 Gpps) — one of many largest packet-rate floods publicly disclosed,” FastNetMon says in a press launch.
“The malicious visitors was primarily a UDP flood launched from compromised customer-premises tools (CPE), together with IoT gadgets and routers, throughout greater than 11,000 distinctive networks worldwide,” the corporate explains.
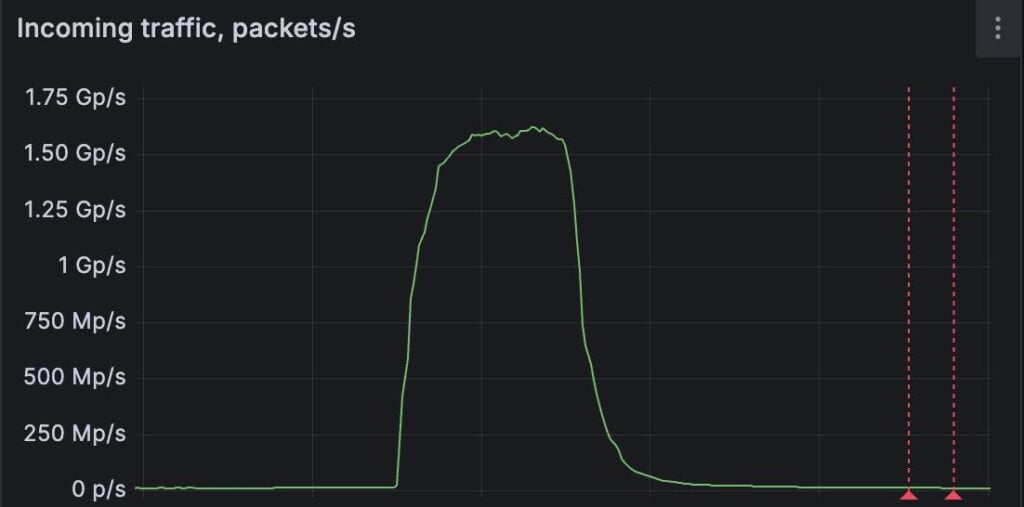
Supply: FastNetMon
FastNetMon didn’t title the focused buyer, however describes it as a DDoS scrubbing supplier. These companies specialise in filtering out malicious visitors throughout DDoS assaults by way of packet inspection, charge limiting, CAPTCHA, and anomaly detection.
The assault was detected in real-time, and mitigation motion was taken utilizing the shopper’s DDoS scrubbing facility. The measures included deploying entry management lists (ACLs) on edge routers recognized for amplification capabilities.
Information of the assault comes simply days after web infrastructure large Cloudflare introduced that it blocked the most important recorded volumetric DDoS assault in historical past, which peaked at 11.5 terabits per second (Tbps) and 5.1 billion packets per second (Bpps).
In each assaults, the purpose was to exhaust processing skills on the receiving finish and trigger service outages.
FastNetMon’s founder, Pavel Odintsov, commented that the development of those large assaults has turn into very harmful, and intervention on the web service supplier (ISP) stage is required to cease this mass-scale weaponization of compromised shopper {hardware}.
“What makes this case outstanding is the sheer variety of distributed sources and the abuse of on a regular basis networking gadgets. With out proactive ISP-level filtering, compromised shopper {hardware} could be weaponised at an enormous scale” – FastNetMon
“The business should act to implement detection logic on the ISP stage to cease outgoing assaults earlier than they scale,” says Odintsov.
46% of environments had passwords cracked, almost doubling from 25% final yr.
Get the Picus Blue Report 2025 now for a complete take a look at extra findings on prevention, detection, and knowledge exfiltration tendencies.

